Skip to content

IamLucif3r · Independent security research

Off the clock, still reading source.

The day job has change control. This is where I just try things.

After hours: LLM guardrails I want to understand by breaking, tools I built because I needed them, CTF boxes, and notes to future me.

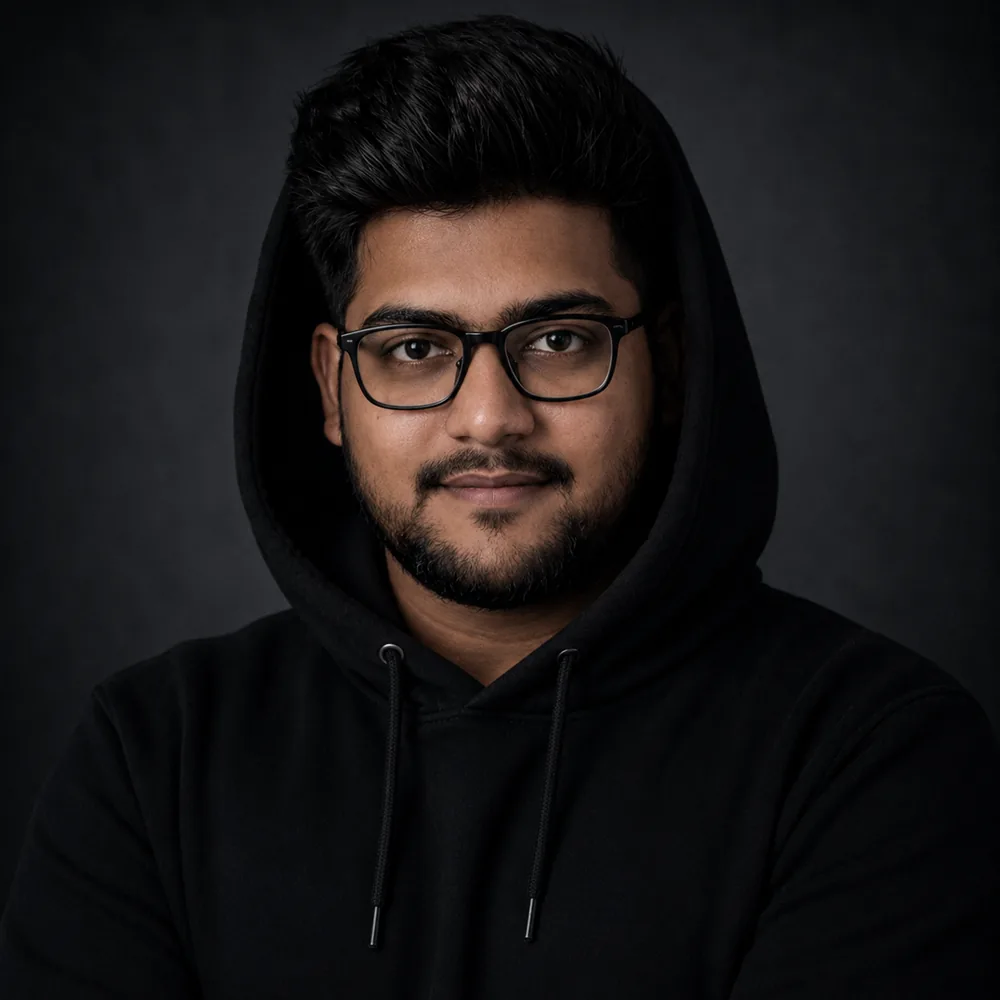
Anmol Singh Yadav, after hours

$ whoami → IamLucif3r

/now

October 2026

Reading
How refusal behaviour is represented inside small open-weight models — and how little it takes to remove it.
Building
SAST-AI-Harness: LLM-driven dataflow tracing and adversarial review on top of open-source SAST engines.
Running
pwnspectrum’s daily ranked security feed — tuning what counts as signal.

Projects

Things I built because I wanted to know how they break.

Featured research · Published

Qwen3-4B Abliterated

What happens to a model’s guardrails when you remove the direction that says no.

Research into LLM refusal mechanisms and model abliteration. I identified the refusal behaviour in Qwen3-4B-Instruct, removed it experimentally, and open-sourced the resulting model alongside a write-up on what it means for guardrails that live inside the weights.

1,000+

downloads on Hugging Face

  • LLM security
  • Refusal mechanisms
  • Abliteration
  • Open weights

Shipping daily

pwnspectrum

A security news feed that ranks what actually matters.

An automated pipeline that scrapes 1,000+ security news articles, scores them for relevance and impact, and publishes the top 20 events as a curated feed.

feed.anmolsinghyadav.comlive

In progress

SAST-AI-Harness

An AI-assisted SAST framework, packaged as a GitHub Copilot Skill.

Orchestrates 10+ open-source security engines, then uses LLM-driven dataflow tracing, attacker-exposure analysis, and iterative adversarial review to find OWASP Top 10, memory-safety, and novel vulnerabilities across multi-language codebases.

  • SAST
  • LLM
  • Copilot Skill

Not public yet

Maintained

AWS Key Hunter

Finds exposed — and still valid — AWS keys in public code.

Searches public GitHub code for exposed AWS credentials and reports only the ones that are valid, so the signal is real exposure rather than pattern matches.

  • Go
  • Secret detection
  • Cloud
GitHub

Maintained

FaviCreep

Creep around the edges of an attack surface via favicons.

Fingerprints favicons to surface shadow assets and forgotten infrastructure an organisation didn’t know was still exposed.

  • Go
  • Recon
  • Attack surface
GitHub

Experimental

Nautilus

A default-deny network firewall for Docker, enforced with eBPF.

Every container starts with no network access; policy grants it. Enforcement happens in the kernel with eBPF, not in a userspace proxy.

  • Go
  • eBPF
  • Docker
  • Zero trust
GitHub

Notes to self

Research notes, dead ends included.

RSS

Signals

Outside the notebook.

  • TryHackMe · Top 1%

    0xD — God Level, through hands-on exploitation and CTF rooms.

    View
  • GRIMMCon

    Spoke on API security and how trust boundaries fail in API-driven systems.

  • Writing · 30K+ readers

    15+ security articles on Medium and InfoSec Write-ups.

    View
  • Community

    Volunteer at DEF CON 9111 Safe Mode.

Signal

Ping me — I usually respond.

Found a bug in one of my tools, broke one of my models, or have a half-formed question about guardrails, eBPF, or containers? Send it.