Skip to content

Anmol Singh Yadav · AI Platform Security Engineer

Then I turn those attack paths into security controls that hold at production scale.

Platform security engineer at ISS STOXX’s Technology Innovation Lab. I design the security architecture for enterprise AI agents, harden the container runtime underneath them, and instrument the kernel to see what actually happens.

  • AI platform security
  • Container isolation
  • eBPF runtime detection
  • Supply-chain security
Portrait of Anmol Singh Yadav
container escape path closed
Fleet-wide
A hardened container runtime rolled out across production Kubernetes clusters and Linux hosts, without operational disruption.
enterprise AI platform secured
Org-wide
Security architecture and threat model for AI agents bridging cloud-hosted models and on-premises enterprise data.
findings to actionable risk
Thousands → hundreds
SBOM-driven vulnerability intelligence across hundreds of repositories, with contextual validation and LLM-assisted prioritisation.
runtime visibility
Kernel-level
eBPF detection for privilege escalation, OOM events, network activity, and sensitive file access on production hosts.

Selected work

A few things that survived contact with production.

Internal work, described at the level I can share publicly: the problem, the controls, and the outcome — without internal names or numbers.

AI platform security

Securing an enterprise AI platform

Security architecture and threat model for an organisation-wide AI platform where cloud-hosted agents act on on-premises enterprise data.

Read the case study

Threat model covered

  • Agent identity
  • Least privilege
  • Tool governance
  • Prompt injection
  • RAG isolation
  • Data exfiltration
  • Sandboxing
  • Egress control
  • Semantic guardrails
  1. Users

    people, federated identity

    Boundary: Identity
  2. AI agents

    cloud-hosted, sandboxed

    Boundary: Guardrails · tool governance
  3. APIs

    governed tools

    Boundary: Gateway · edge · egress
  4. Enterprise data

    on-premises

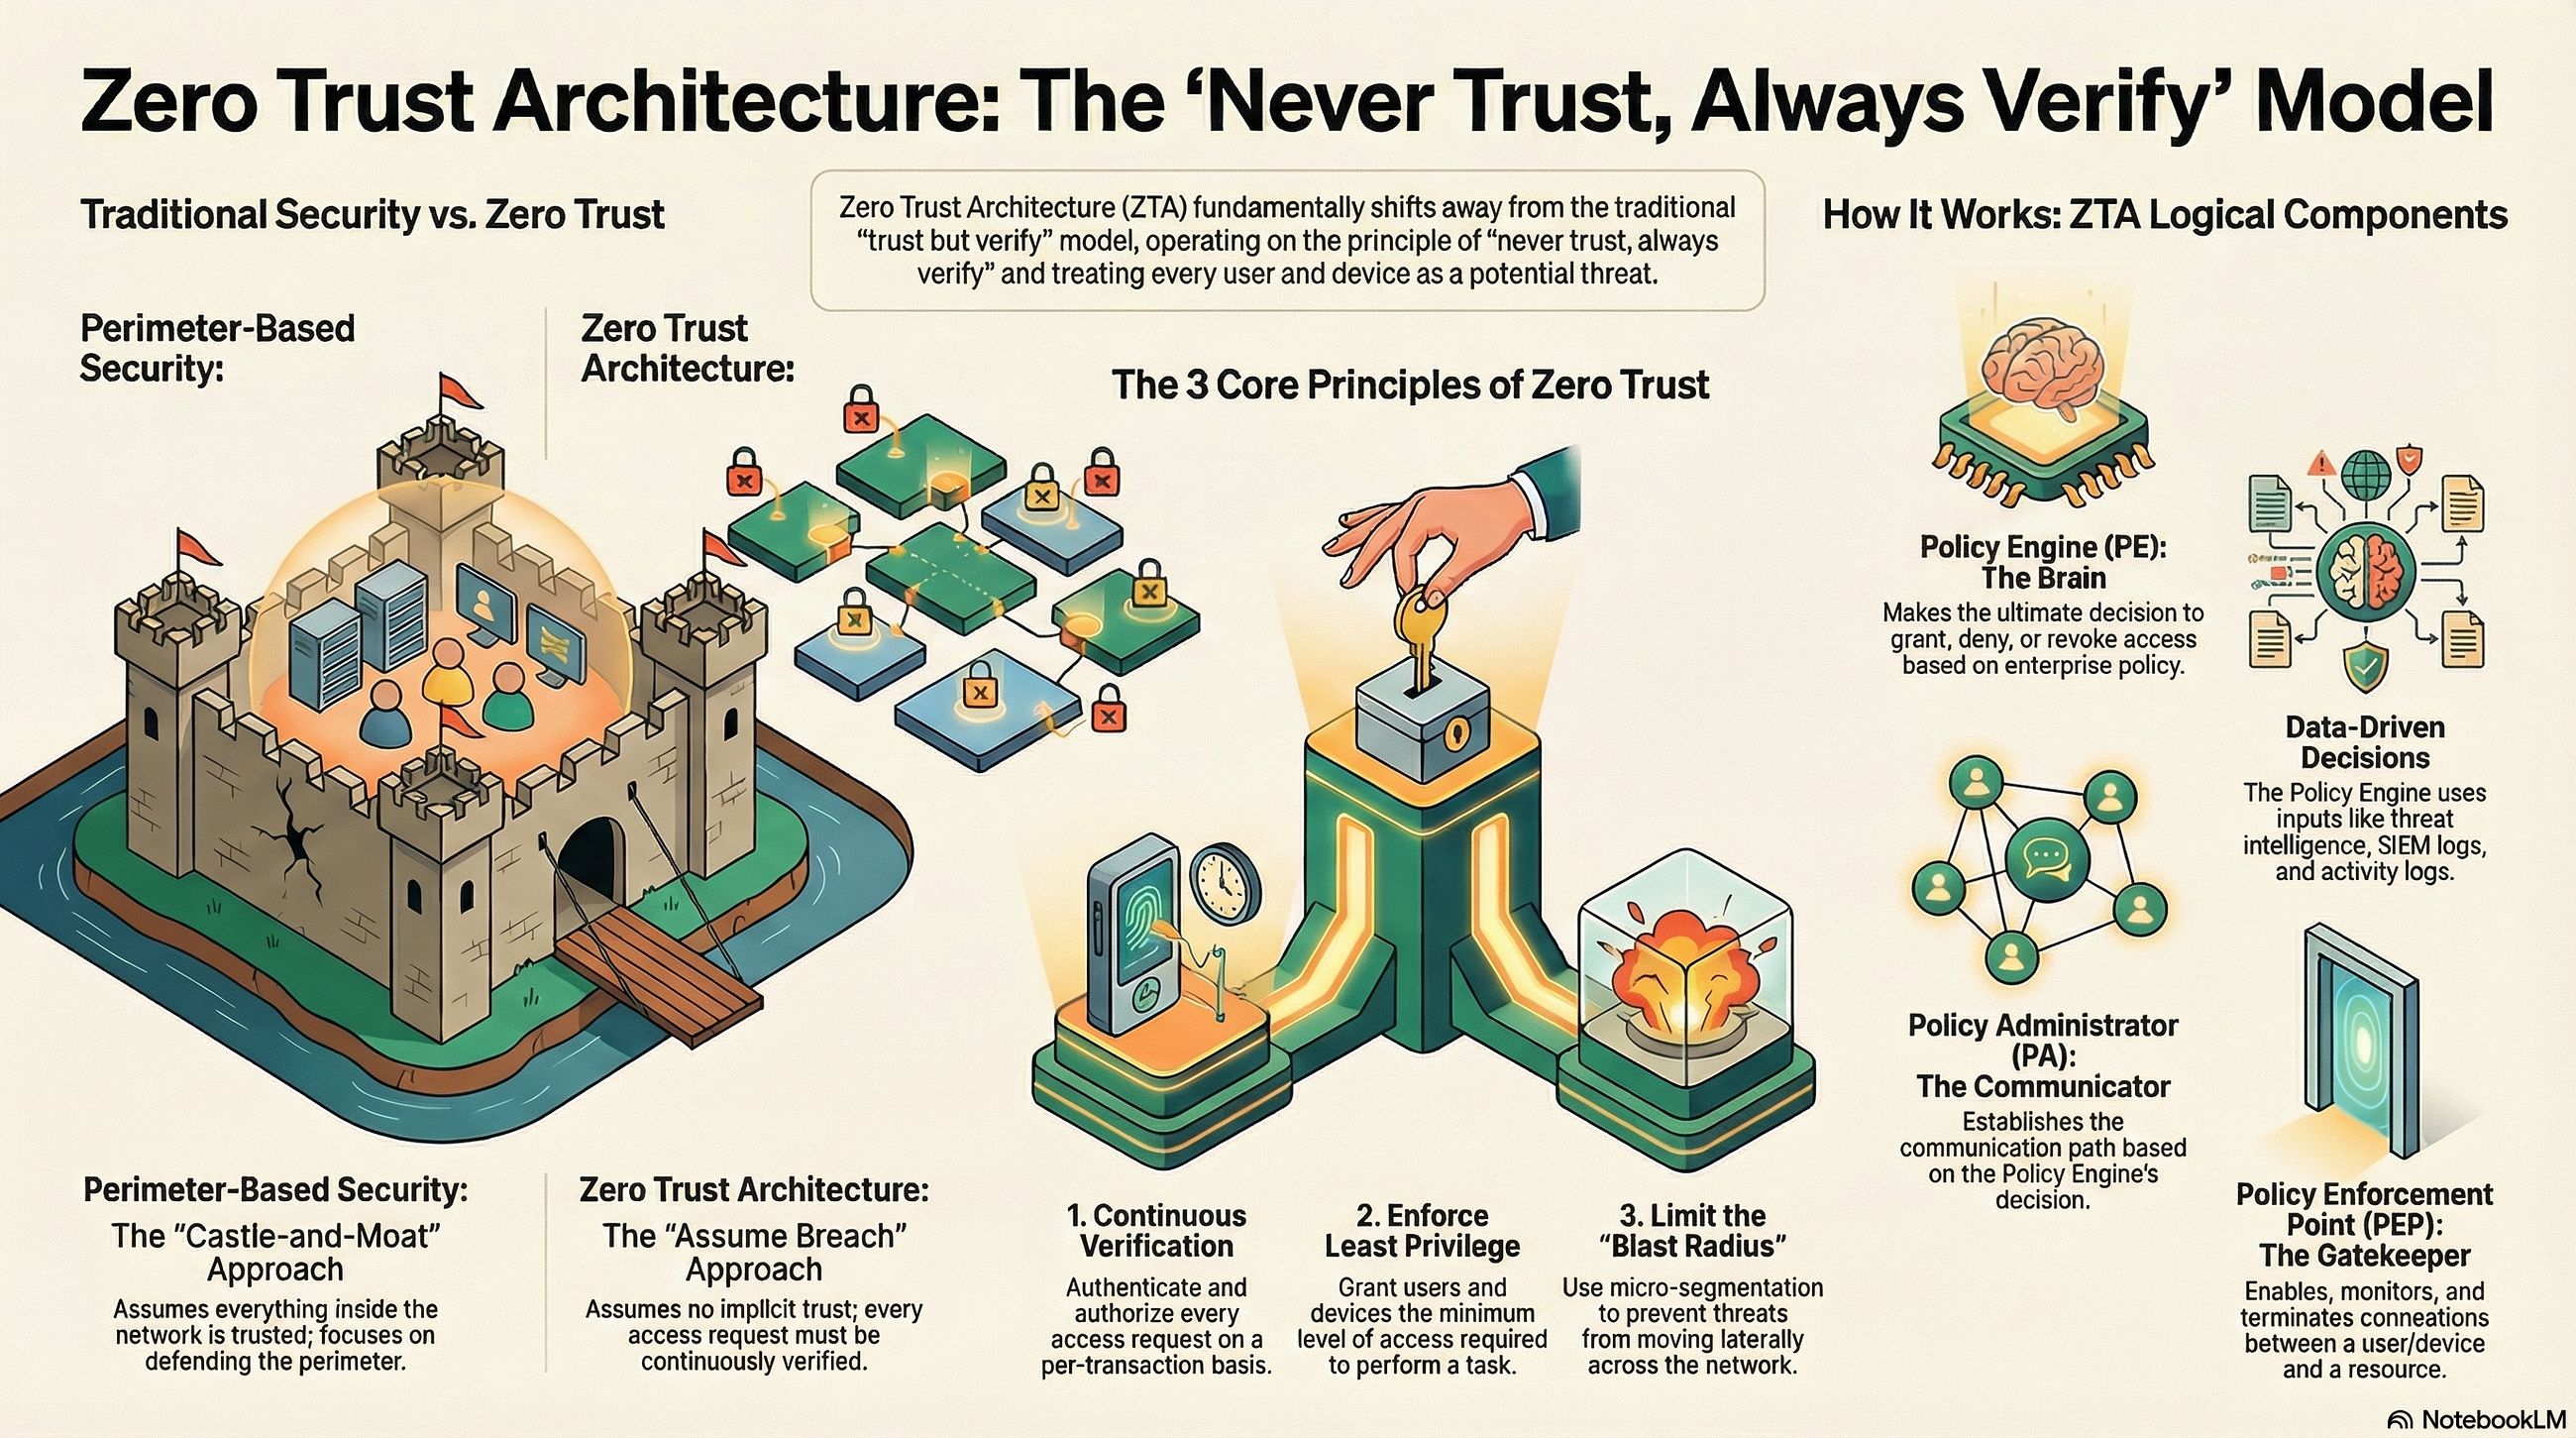
Every hop crosses an enforced boundary — identity, API, network, data, and execution controls.

Container isolation

Closing a container escape path, fleet-wide

Designed and led adoption of a hardened container runtime architecture that removed a validated escape path across production clusters and hosts.

  • Kubernetes
  • containerd
  • runc
  • Kata Containers

Supply-chain security

From thousands of findings to the few that matter

An SBOM-driven vulnerability intelligence system that reduces raw scanner output to actionable risk with contextual validation and LLM-assisted prioritisation.

  • SBOM
  • SCA
  • OSV
  • Threat validation

Runtime security

Seeing what the kernel sees

An eBPF-based runtime detection system for production Linux hosts, built for the questions logs can’t answer honestly.

  • eBPF
  • Linux
  • Syscall tracing
  • Runtime detection

Kubernetes security

kube-explor3r: a Kubernetes security assessment framework

A framework and tool that finds privileged workloads, unsafe capabilities, vulnerable packages, and container escape paths — and keeps watching.

  • Kubernetes
  • Pod security
  • Package scanning
  • Container escape analysis

Expertise

One recurring question: what shouldn’t be reachable?

01

AI Security & Architecture

Treating agents and model execution as untrusted workloads — because they are.

  • Agent identity & isolation
  • Tool governance
  • Prompt injection
  • RAG security
  • Guardrails
  • Threat modeling
02

Cloud & Platform Security

Trust boundaries between users, workloads, APIs, and data — enforced, not documented.

  • GCP Agent Platform
  • Model Armor
  • Workload & Workforce Identity Federation
  • Apigee
  • Cloud Armor
  • Kubernetes
03

Linux & Runtime Security

Instrumenting the kernel to see what actually happens — not what logs claim happened.

  • eBPF
  • Syscall tracing
  • Container escape analysis
  • Privilege escalation
  • Kata Containers
  • containerd / runc
04

Application & Supply Chain

Finding the vulnerabilities that are real, reachable, and worth a team’s time.

  • SAST
  • SCA
  • SBOM
  • OSV
  • Semgrep
  • CodeQL
05

Programming & Systems

Building the tooling, not just configuring it.

  • Go
  • Python
  • Bash
  • C/C++
  • Kafka
  • OpenSearch

The full list, with context, lives on the résumé.

View the web résumé →

Experience

What I actually do, in plain terms.

Most of my work is about boundaries: what a process can reach, what a container can escape, what an agent can actually do versus what its prompt says it can do. eBPF and runtime tracing are usually how I find out the honest answer is “more than expected.”

I write in plain language on purpose. Security writing has a bad habit of sounding impressive instead of being useful, and I’d rather be the second one.

  1. Jan 2023 — Present

    Platform Security Engineer

    ISS STOXX · Technology Innovation Lab

    Security architecture for the enterprise AI platform; container runtime isolation; eBPF runtime detection; SBOM-driven vulnerability intelligence; Kubernetes security assessment.

  2. 2019 — 2023

    B.Tech in Computer Science Engineering

    Vellore Institute of Technology

    Specialisation in Cyber Security & Digital Forensics · CGPA 9.0 / 10

Contact

Let’s talk about the parts that break.

Open to conversations on AI platform security, agent isolation, container and runtime security, and eBPF — as work, as talks, or as research.